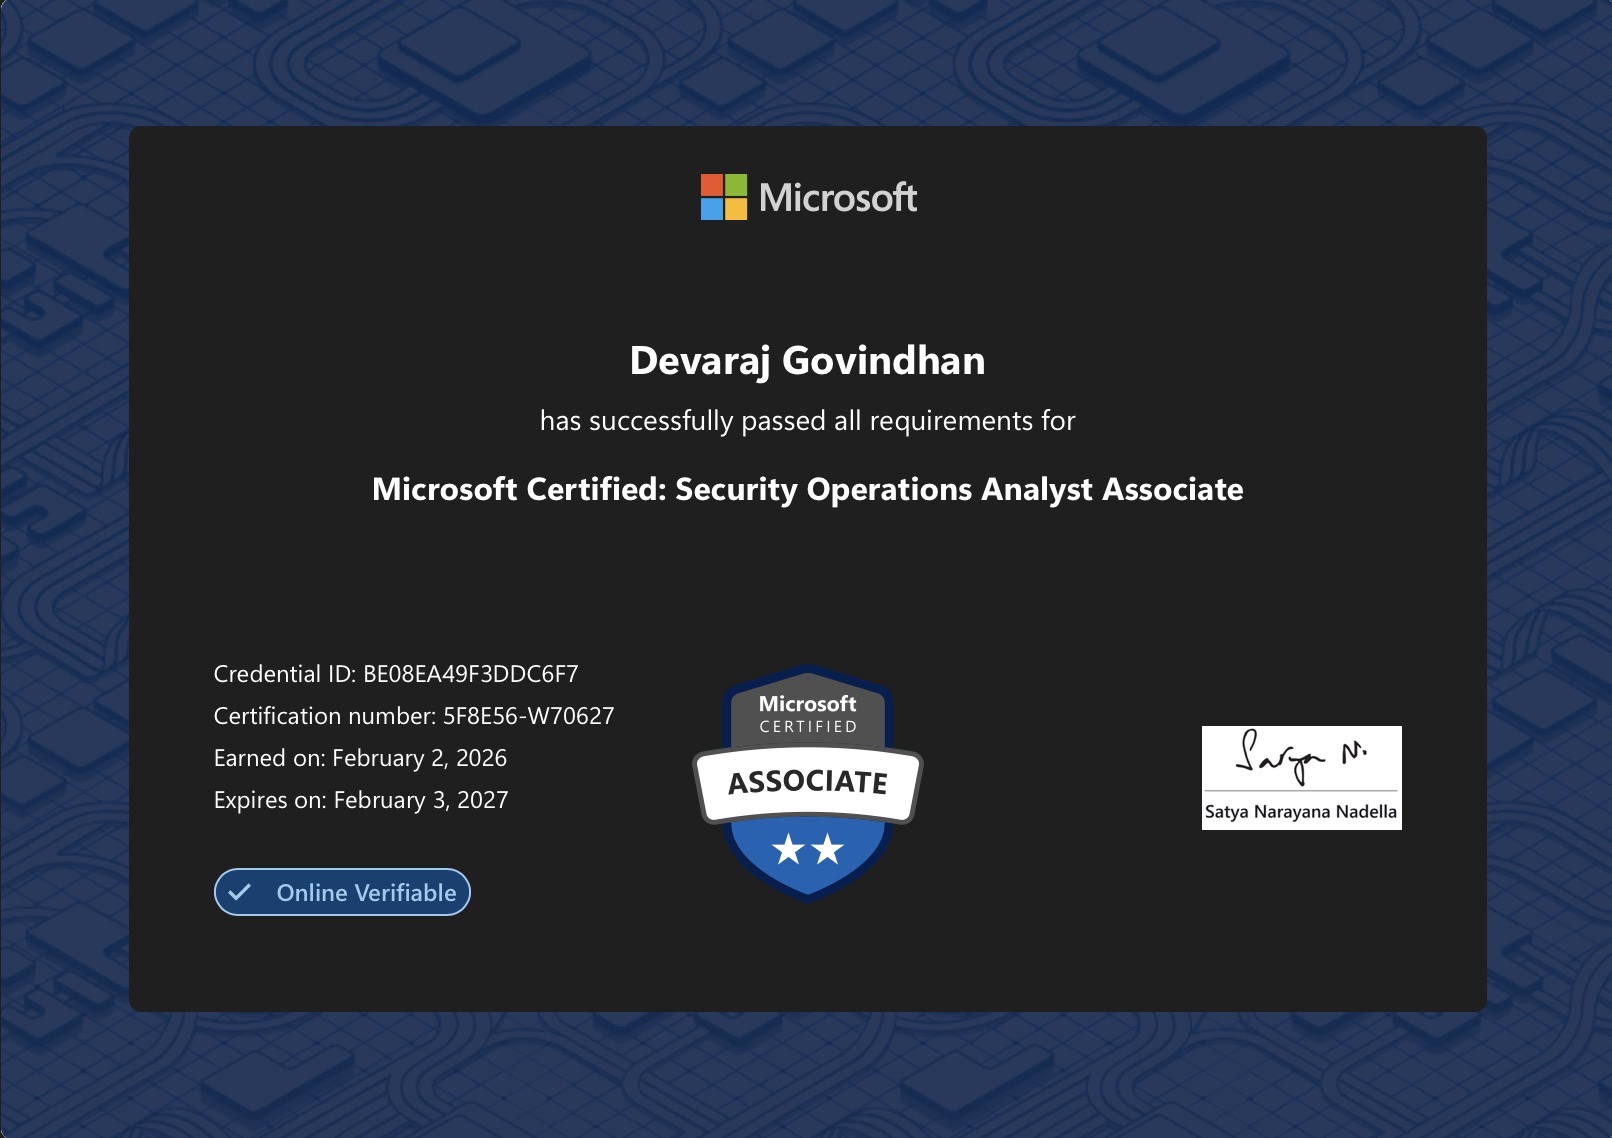
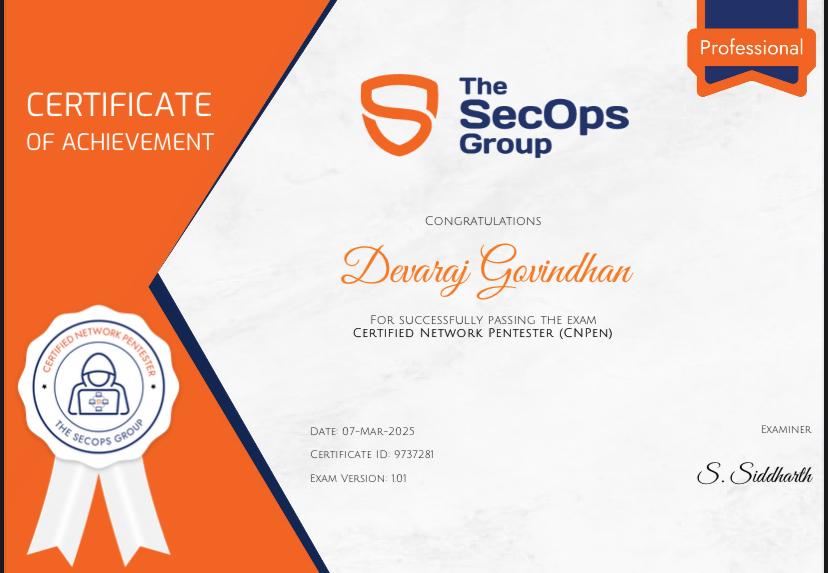
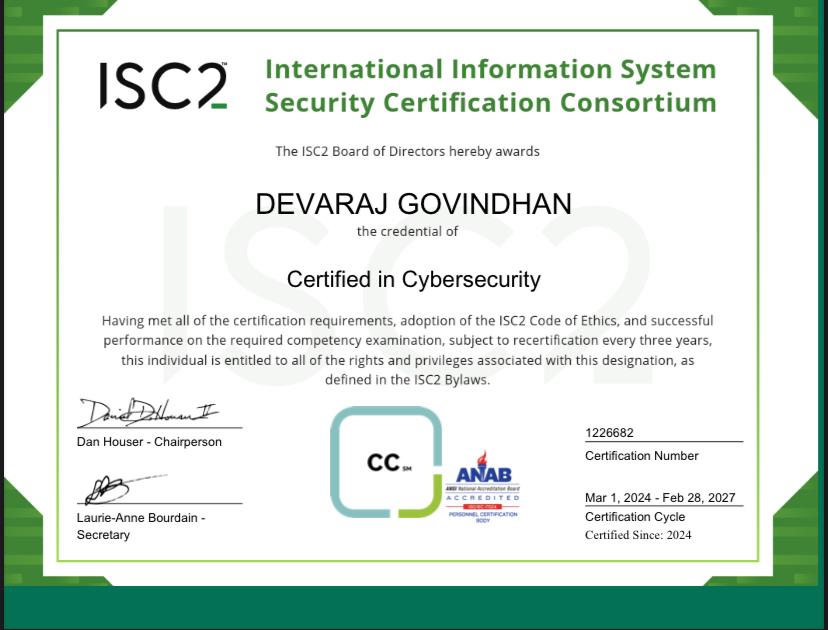
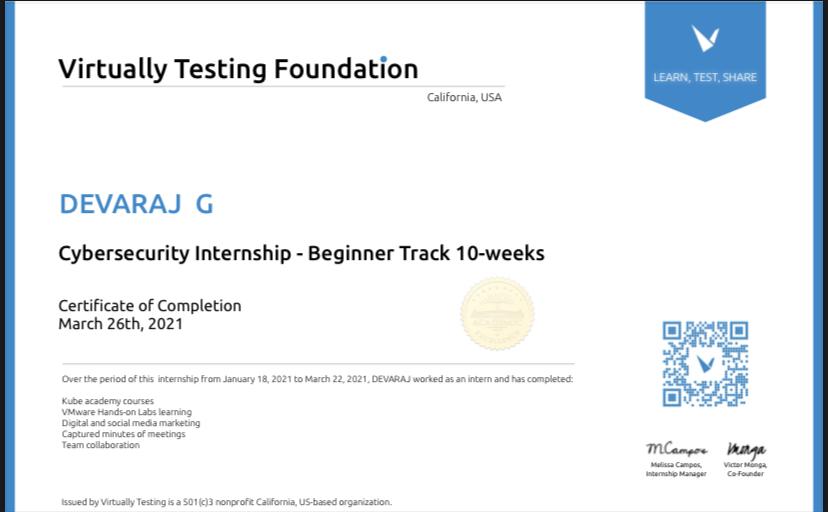
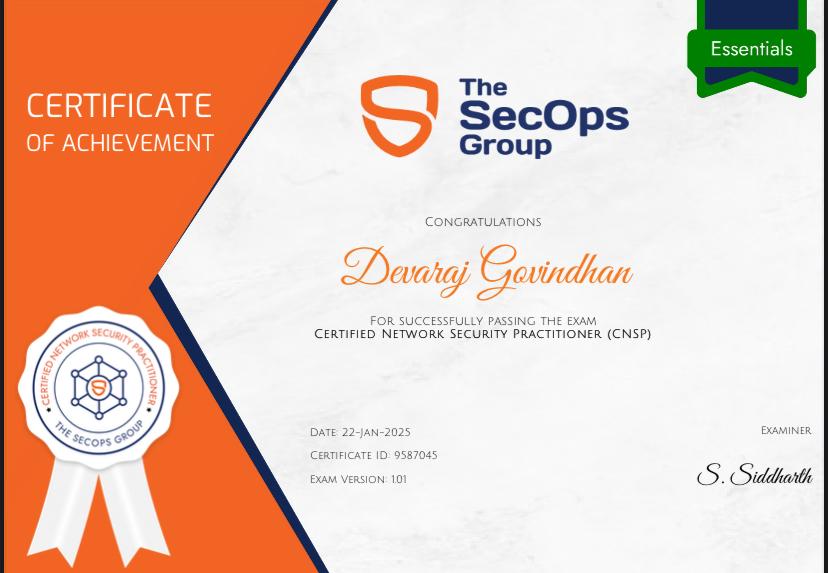
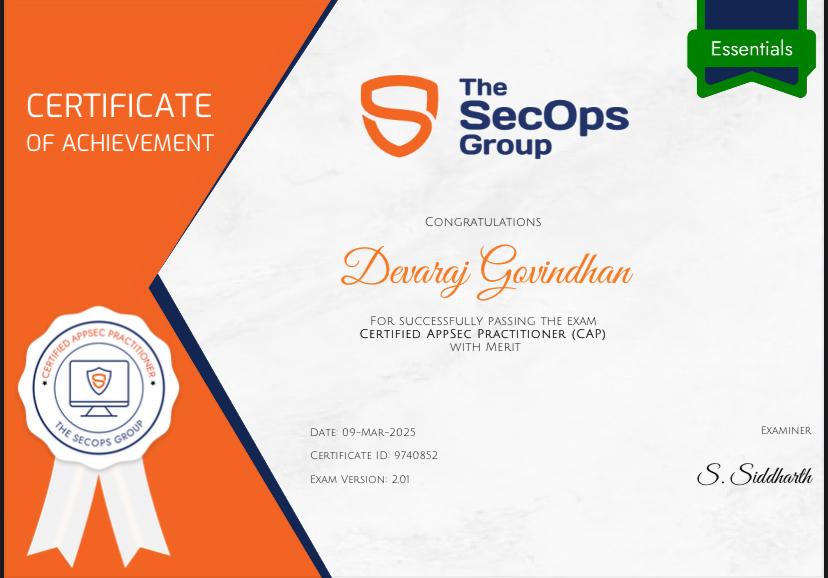
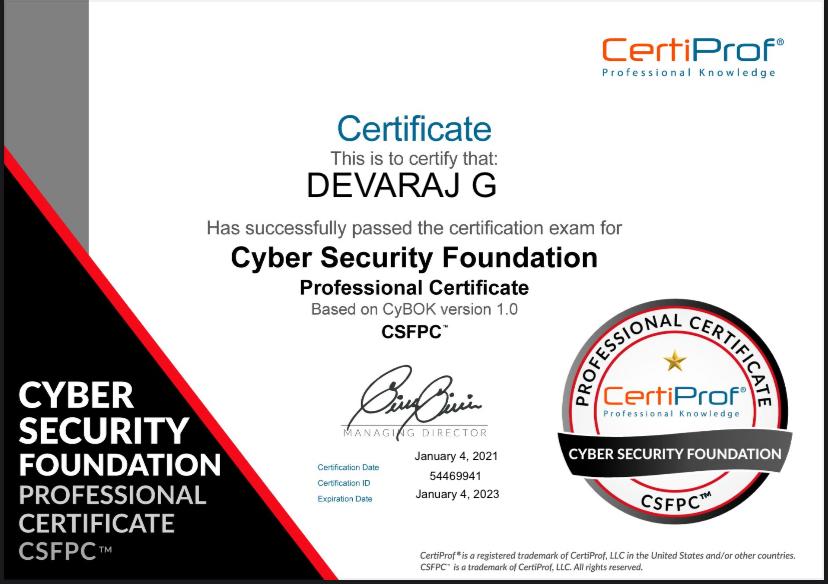
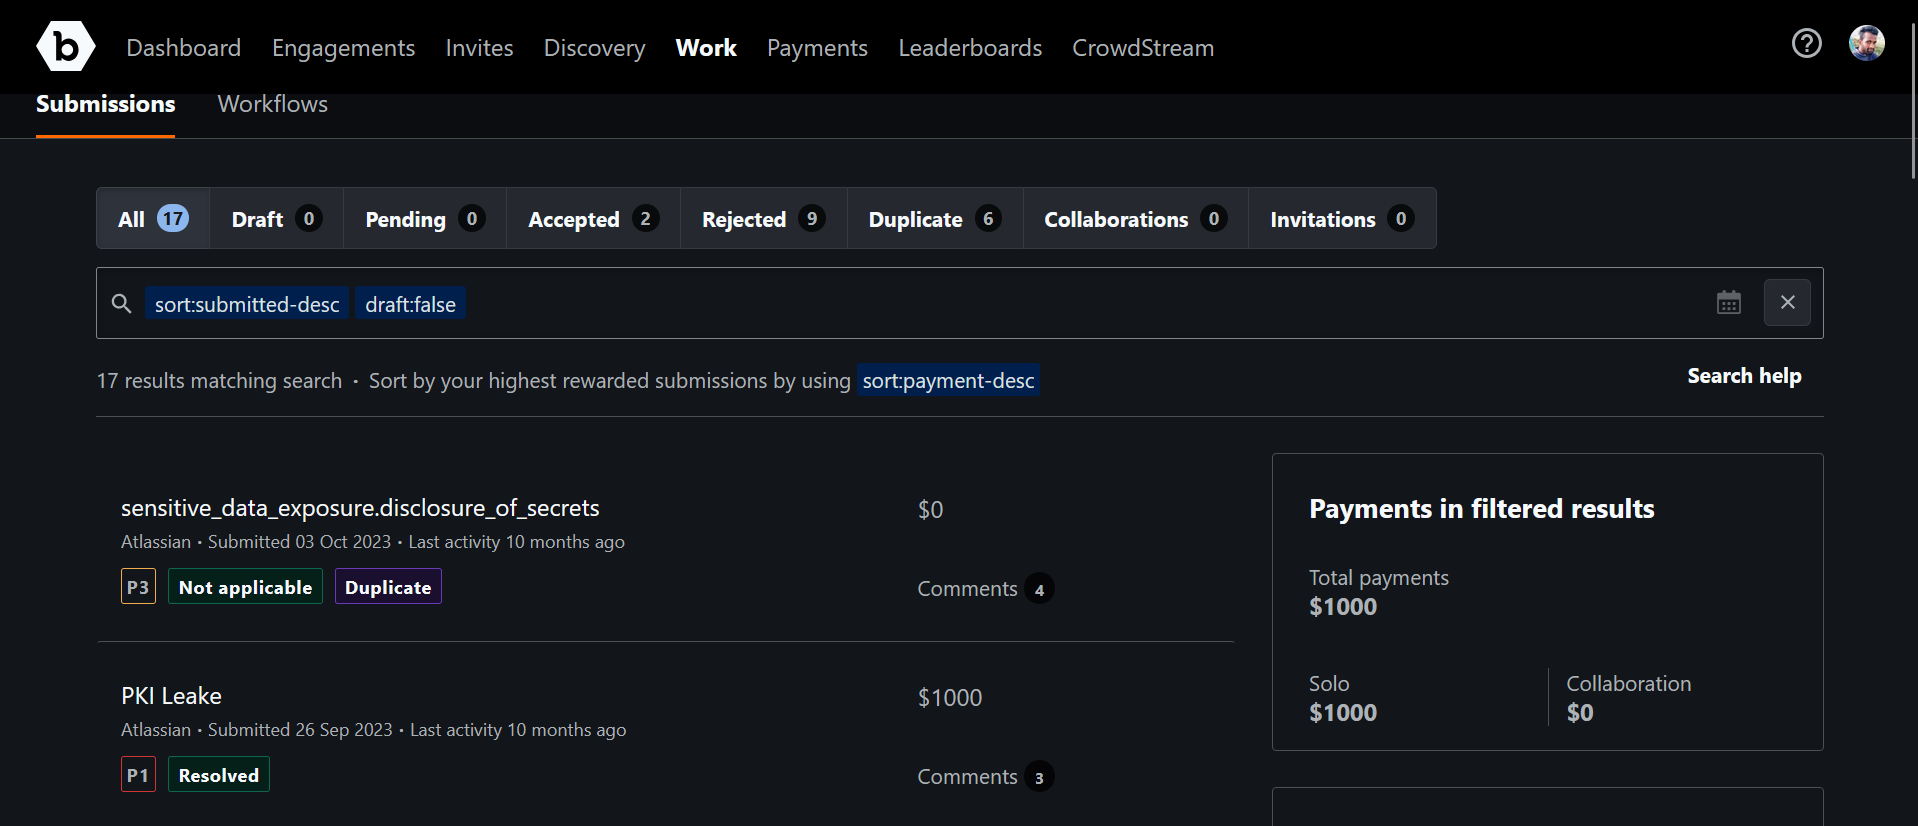
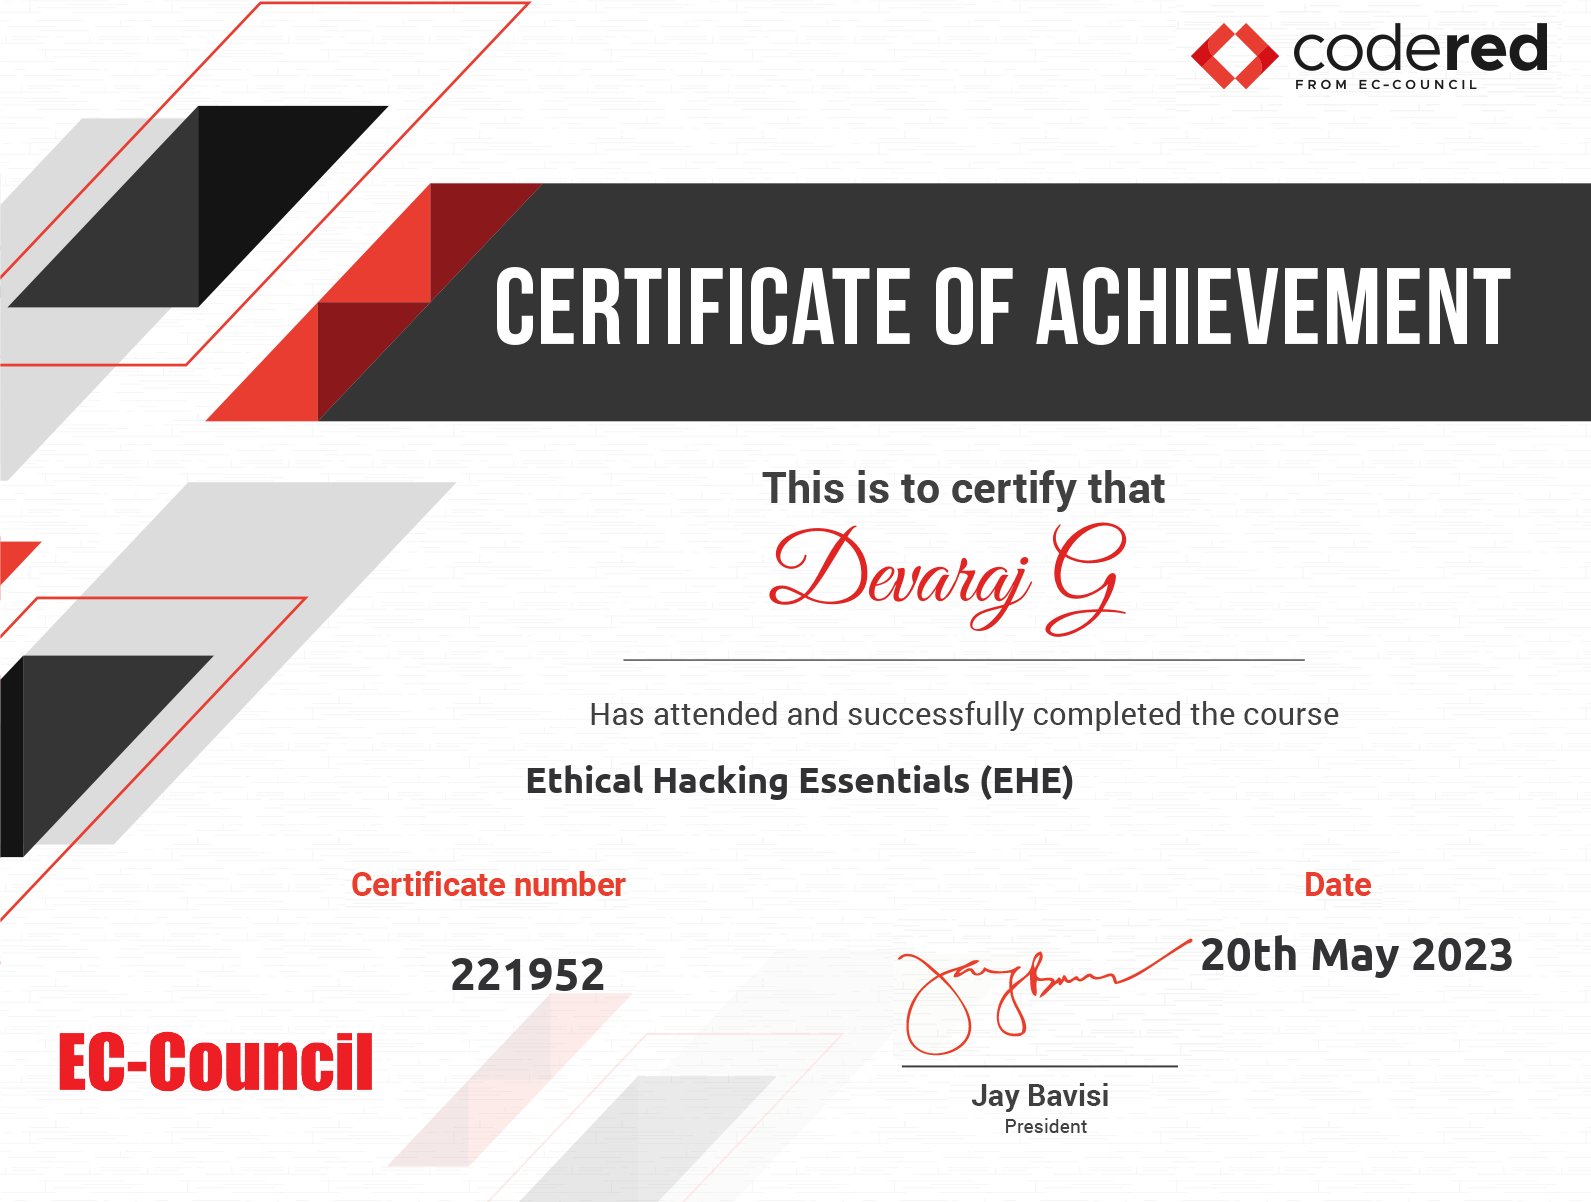
I’m Devaraj Govindhan, a cybersecurity professional with 4.5 years of hands-on experience across Security Operations, Incident Response, Threat Detection, Threat Hunting, SIEM/EDR, Penetration Testing, and Vulnerability Assessment. Currently, I work in Security Operations, where I handle the end-to-end security incident lifecycle from alert triage, investigation, and threat analysis through incident validation, severity assessment, client communication, RCA, and recommendations. I work closely with stakeholders to understand the impact of security incidents, provide actionable recommendations, and support remediation and mitigation activities. My current experience includes SIEM monitoring, EDR investigations, threat detection, alert correlation, incident investigation, Threat Hunting, Root Cause Analysis (RCA), IOC analysis, MITRE ATT&CK mapping, escalation, and security monitoring. I focus on distinguishing genuine security threats from false positives and ensuring that incidents are investigated thoroughly with clear findings and actionable remediation guidance. I have hands-on experience with Microsoft Sentinel, Microsoft Defender, SentinalOne EDR, Crowdstrike EDR, Splunk, Seceon, Wazuh, and other security monitoring technologies, along with analyzing security events, logs, endpoint activity, network indicators, and threat intelligence to identify and investigate potential attacks. My role also involves client-facing communication, where I communicate technical findings, incident impact, investigation results, and recommended remediation steps in a clear and actionable manner. In addition to my technical security experience, I have hands-on experience in ISO/IEC 27001 implementation and internal audits, supporting information security governance and compliance activities. This has provided me with practical exposure to ISMS implementation, risk assessment, security controls, documentation, compliance requirements, audit preparation, and internal control assessments, giving me a broader understanding of information security beyond technical operations. My background in Offensive Security further strengthens my SOC capabilities. Earlier in my career, I worked as a Penetration Tester, performing Vulnerability Assessment and Penetration Testing (VAPT) across Web Applications, APIs, Networks, and Infrastructure. This experience helps me understand attacker methodologies, exploitation techniques, vulnerabilities, and attack paths, allowing me to apply an attacker’s perspective to defensive security operations. I’m passionate about Threat Hunting, Incident Response, Detection Engineering, Threat Intelligence, Vulnerability Research, and Application Security, with a strong focus on continuous hands-on learning through security labs, CTFs, research, and real-world security investigations. I hold certifications including Microsoft Certified: Security Operations Analyst (SC-200), ISC2 CC, Certified Network Pentester, Certified Application Security Practitione, EHE, CEH, CCNA, and MCSE, reflecting my commitment to continuously strengthening my technical expertise across offensive and defensive security. I bring together offensive security experience, SOC operations, threat investigation, and security research to analyze threats from both an attacker’s and defender’s perspective, improve security visibility, and support effective detection, response, and remediation.
Monitor security alerts and events as a Level 1 (L1) SOC Analyst using SIEM and EDR tools. Perform alert triage to identify false positives, benign activities, and potential security incidents. Investigate security alerts to determine impact, scope, and root cause. Initiate remediation and containment actions for confirmed (true positive) security incidents. Prepare Root Cause Analysis (RCA) reports and incident documentation for true positive alerts. Carry out end-to-end implementation of Wazuh SIEM & EDR for clients, including installation, configuration, agent deployment, log onboarding, rule tuning, and dashboard setup. Assist in onboarding log sources, tuning rules, and improving detection capabilities in Wazuh
In my professional journey spanning over 3 years, I've had the privilege to work in diverse areas, acquiring a robust skill set and honing my expertise.
Web Application Security: I've taken a proactive role in Web Application Security, implementing and maintaining best practices and security protocols, guaranteeing the safety of our web applications and the data they handle.
Vulnerability Scanning: Conducting thorough Vulnerability Scanning, I've utilized cutting-edge tools like Nessus to assess and address potential weaknesses, reducing security risks significantly.
Web Security Tools: Finally, my familiarity with Web Security Tools such as Burp Suite has been instrumental in safeguarding our digital assets, particularly web applications, and ensuring their security.
Vulnerability Assessments: I've conducted comprehensive Vulnerability Assessments to proactively identify and address vulnerabilities, bolstering our defense mechanisms. Network Assessments have been a focus of my work, ensuring the reliability and security of our network infrastructure.
Problem Solving: My experience in Problem Solving has been instrumental in addressing complex challenges and finding innovative solutions to a range of issues, demonstrating my analytical and critical thinking abilities.
Vulnerability Management: As a practitioner in Vulnerability Management, I have consistently fortified our organization's security posture by identifying and mitigating vulnerabilities in IT systems, contributing to a robust defense against potential threats.
Security Operations: My role in Security Operations saw me leverage advanced tools such as Wazuh SIEM and XDR solutions. These tools empowered me to monitor, detect, and respond to security incidents in real-time, reinforcing our incident response capabilities and minimizing security risks.
Intrusion Detection Systems (IDS): Intrusion Detection became a core focus as I spearheaded the setup and maintenance of Intrusion Detection Systems (IDS). This effort bolstered our threat detection capabilities, enhancing network security and ensuring data integrity.
Information Technology: As part of my work in Information Technology, I've been at the forefront of managing various IT aspects, ensuring the seamless operation of critical systems.
Web Applications: I have actively contributed to the development and maintenance of secure Web Applications, aligning with our commitment to delivering safe and reliable online services.
Web Hosting: My expertise in Web Hosting has played a vital role in maintaining our online presence and ensuring consistent service availability.
ISO 27001: Compliance with the stringent standards of ISO 27001 has been a top priority, with my work ensuring we meet the requirements of this globally recognized information security framework.
Risk Assessment: My role in Risk Assessment has been pivotal in identifying and mitigating potential threats, thereby fortifying our security measures.
Cloud Computing: In the realm of Cloud Computing, I've adeptly managed and secured cloud-based solutions, ensuring a smooth transition to the cloud while maintaining stringent security standards.
Bitbucket: Collaborative coding using Bitbucket has allowed us to streamline development, emphasizing code quality and security. as well as Implement CI/CD Implementation and maintainance of a web application.
Linux Servers: As a server administrator, I've managed Linux Servers, including the deployment and maintenance of Apache web servers, ensuring a secure and reliable hosting environment.
Microsoft Azure: In the cloud domain, I've managed and secured resources on Microsoft Azure, contributing to a comprehensive cloud security strategy.
IT Hardware Support: My support as a practitioner in IT Hardware Support has been instrumental in the smooth operation of our IT infrastructure, reducing downtime and enhancing overall operational efficiency.
DevOps: My experience in DevOps has involved integrating security measures into our DevOps pipeline, ensuring secure and efficient application delivery.
MCSE: Holding the prestigious MCSE (Microsoft Certified Systems Engineer) certification reflects my proficiency in Microsoft technologies, underlining my value to the organization.
Networking: My expertise in Networking has facilitated robust network administration, supporting network security and performance optimization.
Application Functional Testing: Experienced in Functional Testing, including Software Functional Testing for web applications.
This diverse and comprehensive blend of experience and expertise underscores my dedication to enhancing our organization's security posture and ensuring the confidentiality, integrity, and availability of critical information assets. I remain committed to proactively addressing challenges, safeguarding our digital landscape, and contributing to the ongoing success of our cybersecurity initiatives.
I have experience in hardware and software service, field service, Hewlett-Packard Service Desk, as well as providing PC, laptop, and server support.
My expertise includes Vulnerability Assessment & Penetration Testing, CCNA Switching and Routing, SOC (Security Operations Center), and CEH (Certified Ethical Hacker) training from Prompt Infotech.
2019-2021
Grade:9.01/10
2015-2018
Grade: First class